A hands-on monitoring environment built to collect, detect, and investigate
security activity across AWS and Linux infrastructure. The project combines
host, network, and AWS control-plane telemetry into a centralized detection
and analysis workflow.
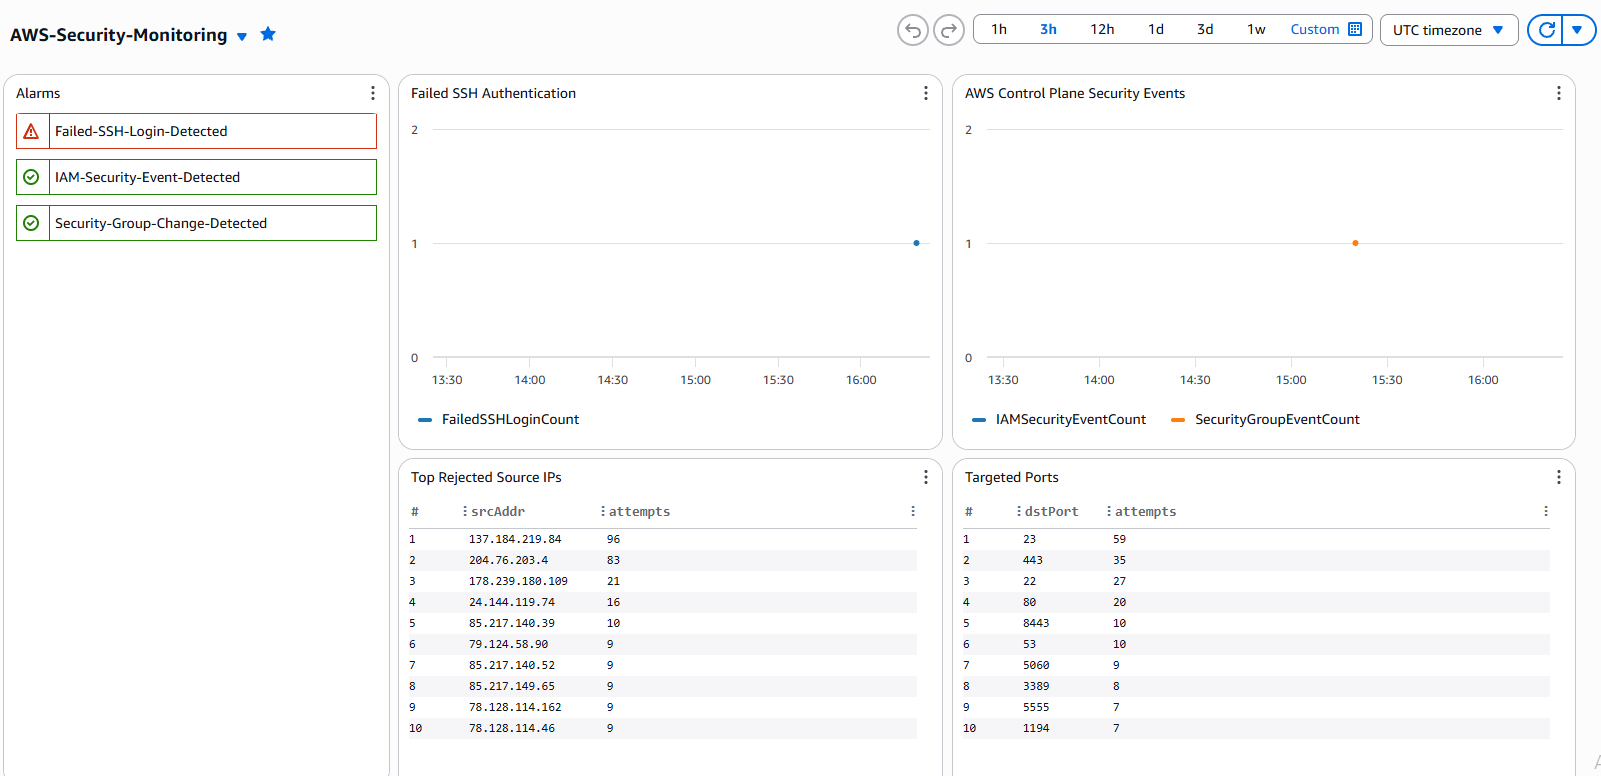
CloudWatch dashboard used to track security alarms, authentication activity,
AWS control-plane events, rejected network traffic, source addresses, and
targeted ports.
HOST TELEMETRY
Linux Authentication
CloudWatch Agent collects authentication and system logs from the
monitoring EC2 instance. Metric filters detect failed SSH
authentication activity and feed CloudWatch alarms.
AWS TELEMETRY
Control-Plane Monitoring
CloudTrail records AWS API activity. Security-focused filters monitor
events involving IAM and security group changes so administrative
activity can be surfaced quickly.
NETWORK TELEMETRY
VPC Flow Analysis
VPC Flow Logs capture accepted and rejected traffic across the VPC,
providing visibility into rejected SSH traffic, source activity,
and commonly targeted ports.
Detection Architecture
Three telemetry sources feed the monitoring pipeline before being used
for alerting, visualization, and investigation.
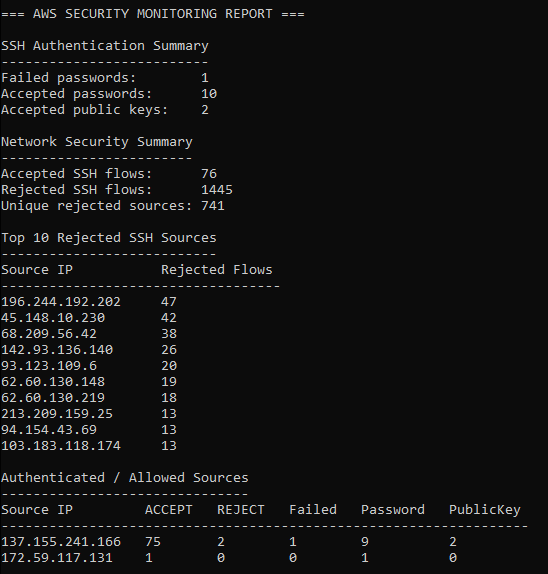
A controlled authentication event was used to verify the complete
collection and detection path from the EC2 host through CloudWatch
and the analysis workflow.
Test Event→auth.log→CloudWatch Agent→CloudWatch Logs→Metric Filter→Alarm→Dashboard→Analyzer